Independent knowledge base software guide Evidence-led Updated 2026

Knowledge Base Governance Framework: Roles, Rules, and Template
A knowledge base governance framework defines who can make decisions about content, what evidence those decisions require, and how the organization follows through. It covers ownership, publishing, review, access, corrections, and retirement—not just a schedule for updating articles. APQC’s governance guidance similarly emphasizes ownership, approval, review, and enforcement.
Start with one knowledge domain and document five things: its accountable owner, authorized contributors, approval rules, review triggers, and escalation route. Then test those rules against actual changes. A policy is useful only when someone can follow it, identify an exception, and show what happened.
The framework below is an adaptable operating model, not a certification standard. It includes decision tables, an inline governance template, and fictional examples showing how to maintain control without sending every correction through an approval queue.
Define what your framework governs
Write a scope statement naming the collection, intended audiences, supported tasks, authoritative sources, and exclusions. For example: This framework governs customer onboarding articles and agent-only onboarding procedures. Product behavior is verified against approved specifications and qualified testing; customer records remain in their designated systems.
Keep related activities distinct. Your knowledge management strategy sets broader priorities. Governance assigns decision rights and controls. The content lifecycle describes how material moves between states. A content audit evaluates existing material and produces findings. A governance policy records the rules, but the framework also includes the people, workflows, and evidence that make those rules operational.
Choose where decisions should sit
Use centralized governance when a small, shared team can make timely decisions for the collection. It simplifies coordination but needs enough capacity to avoid a publishing bottleneck. Use a distributed model when teams can manage separate domains independently, with explicit agreements for shared terminology, links, and overlapping guidance.
A federated model combines shared standards with domain-level decisions. For example, one knowledge base owner maintains common metadata and access rules while product teams validate their own procedures. These are practical operating-model descriptions, not standardized classifications. Choose according to the decisions your organization needs to coordinate.
A small team can combine responsibilities without creating a committee. A larger organization may need a sponsor to resolve cross-team conflicts and fund corrective work. APQC distinguishes knowledge management responsibilities from technical enablement: content, adoption, and user needs require business involvement, while IT manages supporting technology. Administrative access does not make IT the authority on every article’s accuracy.
Assign decision rights without restricting contribution
Separate accountability from authorship. In this proposed model, the knowledge base owner maintains the framework and resolves coordination problems. A domain owner answers for a defined subject area. Contributors draft or correct content, qualified reviewers validate material changes, publishers release approved versions, and platform administrators implement technical controls.
These can be responsibilities within existing jobs. Record who holds each responsibility, their backup, and the route for unresolved decisions. A team name alone is insufficient unless it leads to a monitored queue and someone authorized to act.
Accountability need not mean that only one person can improve an article. The Consortium for Service Innovation’s collective ownership principle places responsibility on people interacting with knowledge to assess and improve it. Preserve that participation while making consequential decisions traceable.
Use a compact decision-rights table
The following table is a proposed allocation. Assign a named role holder for each decision before using it.
| Decision | Authority and execution | Evidence to retain |
|---|---|---|
| Correct wording without changing meaning | An authorized contributor acts under the domain owner’s delegated rules. | Version difference and a brief change reason. |
| Change a procedure | A qualified reviewer validates it; the domain owner authorizes release, directly or through documented delegation. | Applicable source, test result, and approval tied to the version. |
| Change an official policy | The designated policy authority decides; the publisher implements the approved wording. | Policy decision, effective scope, and publication record. |
| Expand the reading audience | The designated disclosure approver authorizes the change; the publisher or administrator applies it. | Audience decision and access-test results. |
| Retire content | The domain owner decides after required records and access checks. | Reason, replacement path, dependencies, and disposition approval where needed. |
| Resolve conflicting sources | The named product, process, or policy authority adjudicates. | Conflicting references, applicability, and the recorded resolution. |
| Change the framework | The knowledge base owner coordinates approval from affected control owners. | Rule change, rationale, approval, and contributor communication. |
For departures or role changes, require a handover of content assignments, open findings, pending approvals, and backups. When ownership is unresolved, the knowledge base owner assigns an interim decision-maker and assesses exposure. Do not automatically delete the content—or leave it available indefinitely without a recorded decision.
Build a content lifecycle with evidence at each transition
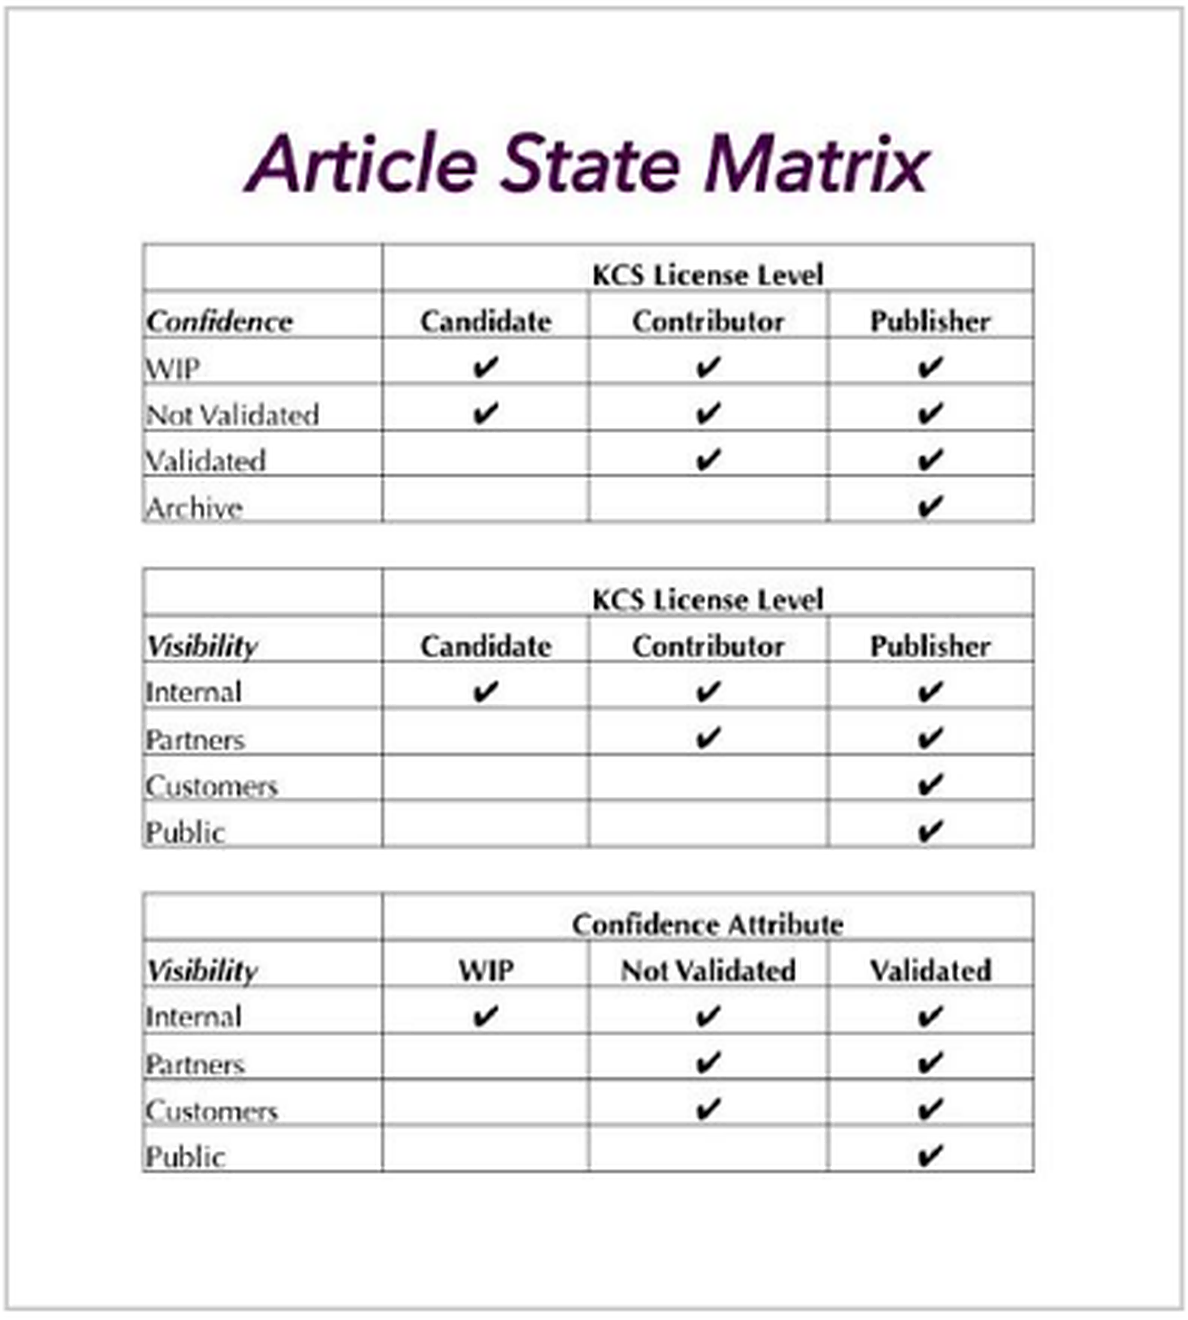
Track workflow status separately from audience and validation confidence. An article can be published for agents only; publication does not prove that every claim was verified. Knowledge-Centered Service (KCS) v6 distinguishes confidence, audience, and governance in its article-state model. The workflow below is a separate implementation example, not a reproduction of that model.
Track the workflow at the version level. One article may have a live version and a proposed revision simultaneously.
| Example stage | Condition for moving forward | Responsible role and record |
|---|---|---|
| Draft or revision | The intended task, audience, sources, and proposed change are identifiable. | Contributor records the draft and change reason. |
| Validation | The checks required by the change’s risk are complete; unresolved concerns are documented. | Qualified reviewer records findings and supporting evidence. |
| Authorized for release | The designated authority accepts the version and its intended audience. | Approver records authorization and any release conditions. |
| Live | The authorized version is available to the correct audience and has passed release checks. | Publisher records the version, release, and access result. |
| Retired from active use | The retirement decision, replacement route, and required preservation are implemented. | Domain owner and administrator retain the decision and verification evidence. |
A low-risk correction can pass these checks within one authorized action; the table does not require a separate person or queue at every stage. A substantive change should not bypass its required validation merely because someone can click Publish.
Where supported, stage revisions separately from live content. Zendesk’s Team Publishing documentation, for example, describes work-in-progress changes that do not affect the published article until released. Availability and permissions depend on the platform and configuration; do not assume equivalent features exist everywhere.
Without staging, use an access-controlled review copy linked to the original, then compare the released text with the approved version. Preserve the previous version according to policy and define how an authorized publisher restores it if necessary. If someone changes substantive content after approval, renew the affected checks rather than treating the old approval as covering new text.
Match approval and review controls to risk
Evaluate the consequence of a wrong change, not just its length. Adding a comma and changing “can be recovered” to “cannot be recovered” are both short edits, but they require different judgment.
| Proposed change class | Review path | Release evidence |
|---|---|---|
| Routine correction | A trained contributor may act within delegated authority when meaning, behavior, and audience remain unchanged. | Change history and a check that the correction introduced no substantive difference. |
| Material procedure change | A qualified reviewer verifies prerequisites, permissions, steps, and expected outcomes before authorized release. | Source reference, applicable environment, and test or validation result. |
| High-consequence or sensitive change | The designated policy, security, or product authority approves the relevant claims and exposure. | Recorded authorization, qualified validation, and access or release checks appropriate to the risk. |
These classes are adjustable controls, not industry-mandated tiers. Publish examples of what falls into each class, and route ambiguous cases to a reviewer. The KCS v6 licensing model provides a useful reference for connecting permissions to demonstrated competence rather than job seniority. It does not make this custom approval table an official KCS workflow.
Provide an emergency correction path
When live guidance could cause serious harm, route the report immediately to the designated incident or content authority. That authority should choose a proportionate interim action, such as replacing an unsafe instruction with an approved warning, restricting the affected article, or directing users to a safe support channel.
Record who authorized the action, the affected version, the reason, and the follow-up owner. Containment and permanent correction are separate tasks. Close the issue only after the replacement guidance and affected distribution paths have been checked.
Combine review methods without treating them as interchangeable
APQC recommends recurring reviews alongside event-based triggers, with frequency adjusted to the content. KCS v6’s “reuse is review” practice emphasizes improving knowledge during actual use instead of reviewing every article simply because it exists. These approaches have different contexts; neither establishes a universal review interval.
For this framework, define the review method by content class. Frequently reused troubleshooting knowledge can be checked in the support workflow. A consequential procedure may also need scheduled verification even when rarely used. Product releases, policy revisions, incidents, reproducible user reports, and ownership changes should trigger an assessment before the next calendar review.
Make verification evidence specific: the reviewer, date, source or test, applicable version, and outcome. Keep last edited, last reviewed, and last verified distinct. Opening an article or correcting its formatting does not establish that its procedure works.
Also separate writing standards from factual validation. The Consortium explains that its Content Standard Checklist is not a technical accuracy review. A strong formatting score must not conceal an unresolved factual defect.
Enforce access and retire content deliberately
Define reading, editing, approving, publishing, and administrative permissions independently. Apply the least-privilege principle described by NIST: grant the access necessary for assigned work. A contributor who can fix wording does not automatically need permission to expose restricted articles publicly.
For public help content, check what an unauthenticated reader can see. For agent-only procedures, test the intended staff group and an excluded role. For internal policies, verify both the audience and the designated policy authority. Use authorized test accounts; a label saying “internal” is not evidence that access is restricted.
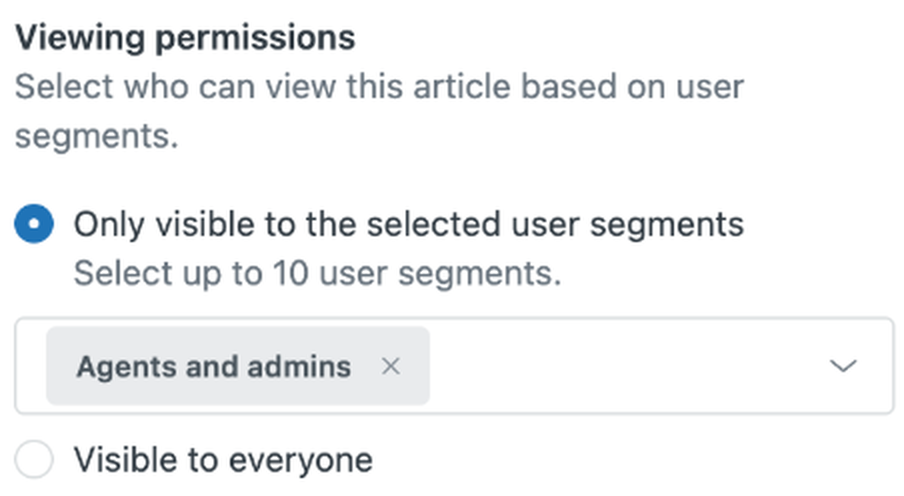
Define retirement terms in your policy. Unpublishing removes a version from its active channel. Archiving preserves material under an agreed access and retention policy. Superseding identifies a replacement. Deletion removes a record through the system’s applicable process. Confirm the platform’s actual behavior rather than assuming these labels guarantee identical outcomes.
Before retirement, check replacement guidance, supported versions, incoming references, translations, training material, and required records. Obtain applicable retention or legal-hold decisions from the responsible organizational authority. This template sets no universal retention period and does not establish regulatory compliance.
Include search and AI distribution in the controls
Maintain a small register of systems that consume the content: internal search, customer search, exports, and artificial intelligence (AI) answer tools. Assign someone to verify whether corrections, withdrawals, and permission changes reach each relevant destination.
Microsoft’s Azure AI Search documentation illustrates why this matters: its documented native token-based permission enforcement is in preview and relies on permission metadata synchronized into the index. Source permission changes are not reflected until the relevant synchronization occurs. This is a product-specific example, not a capability to assume across tools.
For your implementation, test permitted and excluded users, inspect the retrieved sources behind AI answers, and verify withdrawn content through actual queries. Do not close a retirement task merely because the original page disappeared from navigation.
Make unresolved work and exceptions visible
Use one intake route for content reports, with an alternate escalation path for urgent issues. Record the article or gap, observed problem, supporting evidence, consequence, assignee, and next action. Give the reporter a reference and a closure explanation rather than silently marking the issue resolved.
When sources conflict, compare their authority, scope, version, and effective applicability. Route the unresolved question to the designated decision-maker. A newer timestamp is not enough to establish authority. Record the interim treatment while the conflict remains open.
An overdue review should produce an escalation and exposure decision, not an invisible extension. Keep the original due date and record any revised commitment. Assess whether the content can remain available, needs a warning or access restriction, or should be withdrawn.
For an approved exception, retain the affected control, reason, risk, temporary mitigation, authorized approver, responsible owner, expiration or review trigger, and closure evidence. The knowledge base owner may approve editorial exceptions within delegated authority; security or policy exceptions belong to their respective control owners. Expiration must lead to closure, renewed authorization, or escalation—not automatic permanent acceptance.
Copy this knowledge base governance framework template
The following inline template describes a fictional software support team. Its rules are illustrative and can be adapted to an existing policy page or tracking sheet. They are not measured results or a mandatory standard.
Scope and accountability
| Control | Illustrative rule | Implementation record |
|---|---|---|
| Purpose and scope | Govern customer onboarding guidance and agent-only onboarding procedures. Keep customer records and credentials outside this collection. | Collection register naming repositories, audiences, supported tasks, and exclusions. |
| Framework owner | The support operations lead maintains the rules, coordinates unresolved work, and seeks approval from affected control owners. | Versioned policy with approvals, change history, and contributor communications. |
| Domain accountability | The product lead owns product-procedure decisions; the support lead owns agent-workflow decisions. Each has a designated backup. | Responsibility register with current role holders, monitored queues, and escalation contacts. |
| Authority and organization | Use approved product specifications for product claims. The knowledge base owner coordinates shared templates, terminology, and category changes. | Source references, applicable versions, and taxonomy change decisions. |
Publishing, maintenance, and closure
| Control | Illustrative rule | Evidence of execution |
|---|---|---|
| Publishing | Authorized contributors may make meaning-preserving corrections. Procedure changes require qualified validation; audience expansion requires disclosure approval. | Version difference, required approval, and release checks. |
| Review | Check troubleshooting articles during use. Assign scheduled verification where consequence warrants it, and assess affected content after releases or credible reports. | Review method, trigger or due date, reviewer, source, and result. |
| Access | Keep customer guidance public only when approved for disclosure; restrict agent procedures to the designated group. | Permission settings and tests using permitted and excluded roles. |
| Exceptions and retirement | Time-bound exceptions require the relevant control owner’s approval. Retirement requires a replacement or disposition decision and downstream verification. | Exception record or retirement record, with assignee and closure evidence. |
| Monitoring | The knowledge base owner reviews unresolved high-consequence findings, overdue commitments, and expired exceptions, then assigns action. | Issue register, metric definitions, decisions, and follow-up results. |
At article level, retain an identifier, domain owner, audience, applicable scope or version, authoritative reference, workflow status, validation evidence, and review trigger. Use “not verified” where evidence is absent rather than inventing a verification date.
Start with these essential records. Add specialized review, localization coordination, automated routing, or formal cross-team oversight when the collection’s risk and scale justify them—not merely to make the framework look comprehensive.
Test the framework with three worked decisions
These fictional scenarios use the same support-team model. Each shows the trigger, authority, evidence, and condition for closure.
A contributor corrects a harmless typo
An agent notices a misspelled word in an onboarding article. An authorized contributor confirms that the correction changes neither meaning nor a product label, applies it, and records the reason. The domain owner’s delegation permits this without a separate approval queue. The change closes after a version comparison and rendering check.
A deletion procedure contains an unsafe assurance
A report identifies an article claiming that workspace deletion is reversible, while the approved specification says otherwise. The product authority assesses the exposure and authorizes an interim warning or withdrawal. A qualified reviewer verifies the replacement procedure in a safe test environment; the product lead authorizes release.
The record contains the conflicting claim, source, affected version, containment decision, and validation result. Closure also requires checks of related agent instructions and relevant search or AI outputs. Editing the source article alone does not complete the task.
An owner leaves while two instructions conflict
An ownership review finds that an onboarding domain has no current decision-maker and contains conflicting setup instructions. The knowledge base owner obtains an interim appointment from the responsible business leader, records the unresolved claims, and agrees on temporary treatment.
The designated product authority resolves the conflict using applicable specifications and validation evidence, not the most recent page date. Closure requires an accepted ownership handover, corrected guidance, handled superseded references, and an assigned review trigger. Replacing a name in the spreadsheet is not enough.
Measure execution without mistaking it for content quality
Use a small scorecard tied to decisions. The following are proposed measurement definitions, not external benchmarks. Set the reporting scope and preserve comparable periods before judging a trend.
| Measure | Working definition | Decision and limitation |
|---|---|---|
| Ownership coverage | Active articles with a confirmed accountable assignment and working escalation route, divided by all active articles in scope, multiplied by 100, at the reporting date. | Identify unassigned areas. Assignment alone does not prove accuracy. |
| On-time required reviews | Review tasks completed with required evidence by their due dates, divided by all review tasks due in the period, multiplied by 100. | Identify capacity or workflow problems. Preserve original commitments and report approved rescheduling separately. |
| Open high-consequence findings | Count unresolved findings by agreed severity and show the oldest age from first report. | Prioritize exposure and blocked work. Do not reset age when reassigned. |
| Approval turnaround | Median elapsed time from a complete review submission to its decision for completed items in the period, separated by change class. | Investigate delays. Also report open-item age so unfinished work is not hidden. |
| Expired exceptions | Count exceptions past their approved expiration without closure or renewed authorization at the reporting date. | Trigger escalation. A low count does not prove all deviations were recorded. |
Document exclusions and keep them consistent. When a rate’s denominator is zero, report it as not applicable rather than zero performance. Report missing evidence separately from confirmed failure.
Pair process measures with verification: sample approved changes for factual defects, repeat access tests, and observe whether intended users can complete important tasks. Finishing a review demonstrates that a process ran; it does not, by itself, prove the answer is correct. Likewise, page views do not establish successful self-service.
Roll out the framework in one knowledge domain
Use completion criteria instead of assuming every organization can implement governance on the same schedule.
- Choose a bounded pilot. Select a meaningful domain and record its articles, audiences, current owners, known defects, and downstream systems. Finish when the boundaries and baseline are understood.
- Assign authority and configure the minimum controls. Confirm role holders, backups, permissions, review paths, and a shared issue register. Finish when contributors know where decisions belong.
- Train with realistic changes. Practice a routine correction, a consequential update, an access change, and an ownership gap. Finish when participants can follow the rules and explain the evidence required.
- Inspect the results. Check completed records, unresolved findings, delays, and access behavior. Remove unnecessary approvals and strengthen controls that failed.
- Expand and maintain the framework. Add domains after the pilot can handle its decisions reliably. Record policy changes, communicate them, and revisit the framework after material organizational, platform, or risk changes.
A new platform is not the first requirement. Begin with a readable policy, an accountable role register, controlled content storage, and traceable work records. Add automation when it solves an observed routing, enforcement, or visibility problem.
The test of governance is whether the next difficult content decision has a clear path. Someone should know who can act, what must be checked, what happens when the rule cannot be followed, and how the team will confirm the issue is resolved.
Sources verified: November 3, 2026.


