Independent knowledge base software guide Evidence-led Updated 2026

Industry-Specific Knowledge Base Software: Requirements, Industries, and Selection Guide
Industry-specific knowledge base software is a knowledge platform designed or configured around the terminology, roles, workflows, risks, systems, records, and delivery conditions of a particular sector. Its value is not that an industry name appears on the vendor’s website. Its value is that the deployed system can deliver the correct approved guidance to the correct person, in the correct context, while preserving permissions, version history, accountability, and evidence.
An organization does not always need a product built exclusively for its industry. A configurable general platform may be sufficient when it can support the required metadata, workflows, identity model, search behavior, integrations, retention rules, and frontline experience. Other organizations may need a vertical product, a knowledge module inside an existing business suite, or a composable architecture connecting several specialized systems.
The correct choice depends on the cost of a wrong answer. If incorrect or unauthorized guidance could expose protected information, create a safety incident, violate a records obligation, cause a financial error, or send a user into the wrong procedural or jurisdictional path, industry fit should be evaluated as an operating requirement rather than a marketing preference.
Information reviewed on November 20, 2026.
Industry-specific knowledge base software at a glance
| Solution pattern | Best fit | Primary advantage | Primary tradeoff |
|---|---|---|---|
| Vertical industry product | One sector with specialized workflows, terminology, and records | Built-in domain model and industry-oriented controls | Higher lock-in and less flexibility outside the target industry |
| Configurable general knowledge base | Organizations that can model their requirements through metadata, permissions, workflows, and APIs | Broader flexibility and easier cross-department adoption | Configuration, governance, and integration work remain with the customer |
| Knowledge module inside an existing suite | Teams centered on CRM, ITSM, contact center, QMS, DMS, or another core platform | Knowledge is close to the workflow and identity model already in use | The knowledge experience may inherit the suite’s licensing, search, and design constraints |
| Composable architecture | Enterprises with several systems of record, specialized search, and AI requirements | Each layer can use the service best suited to its job | More integration, synchronization, observability, and administration effort |
| Custom-built solution | Requirements that cannot be satisfied safely through configuration or integration | Maximum control over domain behavior | Development cost, long-term maintenance, security responsibility, and upgrade risk |
The first decision is therefore not “Which vendor has the longest feature list?” It is “Which operating model can represent and enforce our real industry requirements without creating unmanageable customization?”
What makes a knowledge base genuinely industry-specific?
A genuine industry fit appears in the deployed content model and workflow. It should be possible to represent the conditions that change the correct answer, such as role, competency, product, asset, site, patient or customer category, matter, jurisdiction, contract, plan, version, effective date, or sensitivity level.
Industry-specific software should also support the evidence needed to govern that answer. Depending on the use case, this may include ownership, approval history, effective dates, source authority, training acknowledgment, audit records, retention class, escalation boundaries, and relationships to a system of record.
A product is not industry-specific merely because it:
- Publishes a landing page for the industry.
- Includes a few industry-themed templates.
- Lists companies from that sector as customers.
- Displays a security or compliance badge.
- Uses industry terms in its marketing copy.
- Connects a generic chatbot to uploaded documents.
A better test is whether the platform can express the industry’s operating boundaries, prove how a current answer was approved, prevent unauthorized retrieval, integrate with the appropriate systems, and produce useful evidence during an audit, investigation, incident, or content review.
Start with the knowledge problem, not the product category
APQC recommends selecting knowledge-management tools by starting with the business and user problem, then matching capabilities to workflows, governance, the existing digital environment, budget, and operating capacity. It also cautions that unnecessary customization can increase cost and maintenance difficulty.
Use a risk-based test before assuming that specialized software is necessary.
- Could an incorrect answer harm a person, asset, customer, account, legal matter, service, or regulated process?
- Could the system expose protected, privileged, confidential, payment, student, health, or proprietary information?
- Do different roles or competency levels require different instructions?
- Do product version, machine, location, contract, customer plan, or jurisdiction change the correct procedure?
- Must the organization prove which version was approved and effective at a past date?
- Do users work under time pressure, in the field, on shared devices, or with unreliable connectivity?
- Must users acknowledge, attest to, or complete training against a specific version?
- Do records-retention, legal-hold, or audit requirements apply?
- Will search, a chatbot, an AI assistant, or RAG system retrieve and summarize the content?
- Must the system refuse or escalate when no approved answer exists?
- Does knowledge need to remain connected to a sector-specific system of record?
A standard wiki or general knowledge base may be enough when the content is low risk, the audience is relatively homogeneous, sensitive case data is excluded, integrations are limited, the collection is small and stable, and users can easily escalate unusual decisions to a qualified person.
Vertical product, configurable platform, suite module, or composable architecture?
Choose a vertical product when the domain model is the main constraint
A vertical product can be useful when the sector requires specialized objects, workflows, review states, terminology, or integrations that would otherwise require extensive custom development. Examples include quality-document workflows in life sciences, asset-specific procedures in industrial environments, or matter-oriented knowledge in legal services.
The buyer should still verify whether those built-in workflows match the organization’s actual responsibilities. A preconfigured process can reduce implementation effort, but it can also force the organization into a vendor-specific model that is difficult to change or extend.
Choose a configurable platform when the operating model can be expressed through configuration
A general platform may become industry-specific in practice through controlled metadata, custom roles, approval workflows, audience rules, integrations, search filters, and documented administrative processes.
This approach is strongest when the organization has the skills and ownership required to design and maintain the configuration. It is weaker when critical controls depend on custom scripts, undocumented conventions, or administrators remembering to perform manual checks.
Choose a suite module when workflow proximity matters most
A knowledge module inside CRM, ITSM, a contact-center platform, a QMS, or another core suite can reduce context switching. Agents or employees may be able to search, suggest, reuse, and improve content without leaving the system where the work occurs.
The tradeoff is that the suite’s knowledge module may be optimized for that workflow rather than for every audience, publishing channel, documentation type, or public-help-center requirement.
Choose a composable architecture when no single platform should own every responsibility
A composable architecture may use one system for governed authoring, another for records or quality control, an identity provider for access, enterprise search for discovery, and a permission-aware AI layer for retrieval and answers.
This model avoids forcing one product to become a weak substitute for several specialized systems. It also creates more integration risk. Ownership, synchronization, permissions, failure behavior, deletion, and audit evidence must be defined across the complete architecture.
Industry requirements differ for operational reasons
The following examples are discovery prompts, not universal compliance requirements. An organization should confirm the rules, contracts, risks, and standards that apply to its own activities.
| Industry | High-value knowledge | Context that changes the answer | Controls to test first | Systems and delivery |
|---|---|---|---|---|
| Healthcare | Privacy procedures, clinical-system downtime guidance, administrative workflows, billing and support operations | Role, facility, service line, patient-access context, emergency state | Authorized access, audit activity, integrity, authentication, separation of reusable guidance from patient records | EHR or health-administration integration, secure internal delivery, mobile access |
| Financial services and insurance | Product guidance, account and claims operations, customer communication, supervised procedures | Entity type, product, account, jurisdiction, record category, contract | Time-stamped history, reliable export, retention, legal hold, approval evidence | CRM, policy systems, claims systems, records systems, secure communication workflows |
| Manufacturing and industrial service | SOPs, work instructions, lockout procedures, maintenance, troubleshooting, quality checks | Machine, component, site, shift, product revision, energy source, worker authorization | Current revision, equipment scope, warnings, training, approval, offline and shared-device behavior | MES, PLM, CMMS or EAM, QMS, QR or barcode access, shop-floor devices |
| Legal services | Precedents, clause banks, matter playbooks, intake guidance, research notes | Client, matter, practice area, jurisdiction, privilege, ethical wall | Matter-level permissions, confidentiality, provenance, conflicts, controlled reuse | Legal DMS, matter management, document assembly, identity and ethical-wall systems |
| Industry | High-value knowledge | Context that changes the answer | Controls to test first | Systems and delivery |
|---|---|---|---|---|
| Education | Student services, faculty procedures, records requests, enrollment and financial-aid guidance | Student or parent role, institution, program, academic period, disclosure authority | Audience separation, records access, disclosure logging where applicable, accessibility | SIS, LMS, identity, case management, public and authenticated portals |
| Government and public sector | Public guidance, internal procedures, operational playbooks, records and service-delivery instructions | Agency, mission, information category, role, authorization boundary | Identity, logging, secure configuration, records, accessibility, agency authorization responsibilities | Identity platforms, records systems, approved cloud services, internal and public portals |
| Life sciences | Controlled procedures, quality documentation, work instructions, training material | Product, site, process, batch context, effective version, predicate-rule scope | Approval, effective date, version history, audit evidence, signatures where applicable | QMS, LMS, laboratory and manufacturing systems, validated workflows where required |
| Energy, utilities, aviation, construction, and field service | Asset procedures, emergency guidance, inspection, repair, maintenance, site instructions | Asset, location, environment, worker qualification, connectivity, operating condition | Current version, offline access, warnings, escalation, competency, synchronization | Asset registry, EAM or CMMS, mobile devices, QR codes, offline field applications |
Translate official requirements into testable software controls
Healthcare: access, activity, integrity, and authentication
The HHS summary of the HIPAA Security Rule describes technical safeguards that include access control, audit controls, protection against improper alteration or destruction, and procedures to verify identity for systems maintaining electronic protected health information.
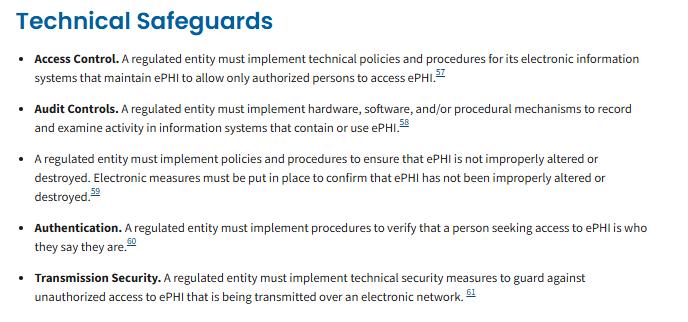
This does not mean every healthcare knowledge article should contain patient information. In many cases, the safer architecture is to keep reusable guidance in the knowledge base while retrieving case-specific information from the authorized health system only when the user’s workflow requires it.
Financial services: record history may matter as much as the current page
Requirements vary across financial entities and activities. For broker-dealers covered by the relevant rules, the SEC’s electronic recordkeeping amendments allow either the established WORM approach or an audit-trail alternative capable of recreating an original record after modification or deletion.
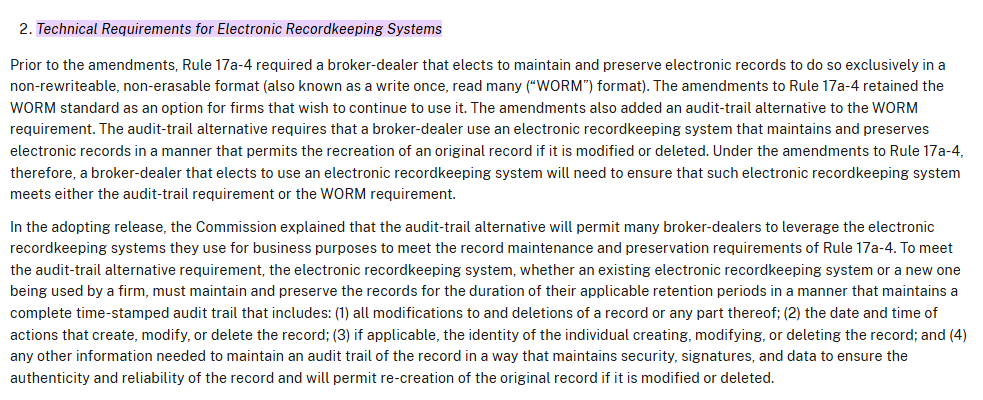
A general article-version list should not be assumed to provide that records capability. Buyers must distinguish collaborative version history from a complete time-stamped audit trail, approved retention, legal hold, reliable export, and reconstruction requirements.
Manufacturing: the correct instruction may depend on the exact machine
OSHA’s control-of-hazardous-energy standard requires energy-control procedures to be developed, documented, and used for covered servicing and maintenance activities, subject to a defined exception.
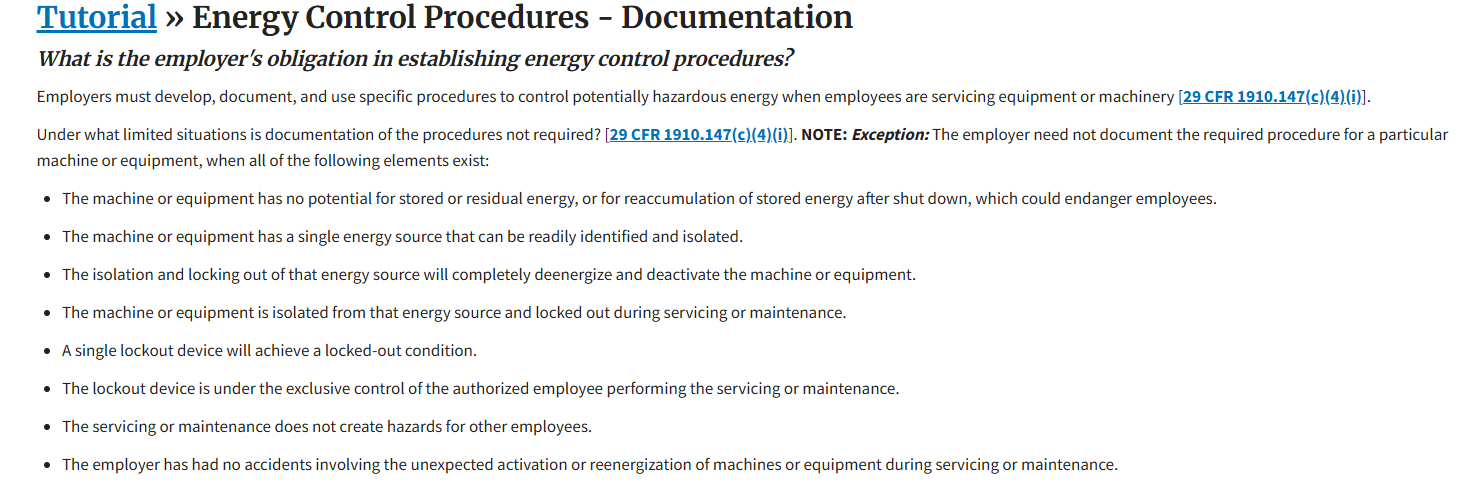
That makes machine, equipment, energy source, step sequence, authorized-worker role, and current revision meaningful knowledge attributes. A generic article titled “Lockout procedure” may be unsafe if several machines require materially different isolation steps.
Legal services: reuse must preserve confidentiality boundaries
ABA Model Rule 1.6 states that lawyers must make reasonable efforts to prevent unauthorized access to or disclosure of information relating to client representation. Jurisdictions adopt and apply professional rules differently, so the applicable obligations must be verified.
For software evaluation, the practical questions include whether permissions can follow matters and ethical walls, whether search snippets and AI answers respect the same boundaries, and whether precedents can be reused without exposing client-specific facts.
Education: guidance and student records should not be confused
FERPA provides parents and eligible students rights relating to education records, including access and control over certain disclosures of personally identifiable information. Some disclosures also require records of access or disclosure, subject to exceptions.
An education knowledge base may publish general procedures for records requests without becoming the repository for each student’s education records. Audience rules should also distinguish students, parents, faculty, staff, and administrators where the correct guidance differs.
Government: cloud certification does not replace agency authorization
Current FedRAMP guidance describes a shared-responsibility model: certification provides reusable evidence for the cloud service, while the agency remains responsible for authorizing the federal information system that uses it, including the information, configuration, integrations, and agency-operated controls.
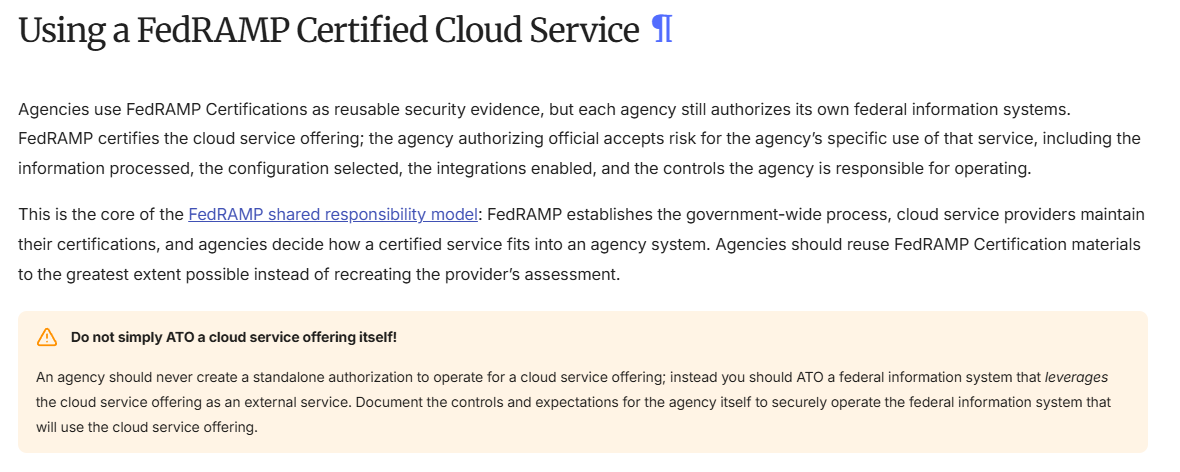
A buyer should therefore examine the certified service and the intended deployment together. Identity, logging, records, privacy, integrations, secure configuration, and ongoing monitoring remain part of the agency’s decision.
Life sciences: determine whether the electronic record is actually in scope
The FDA’s guidance on 21 CFR Part 11 explains that applicability depends on the records and signatures required by underlying predicate rules and how the organization relies on electronic records.
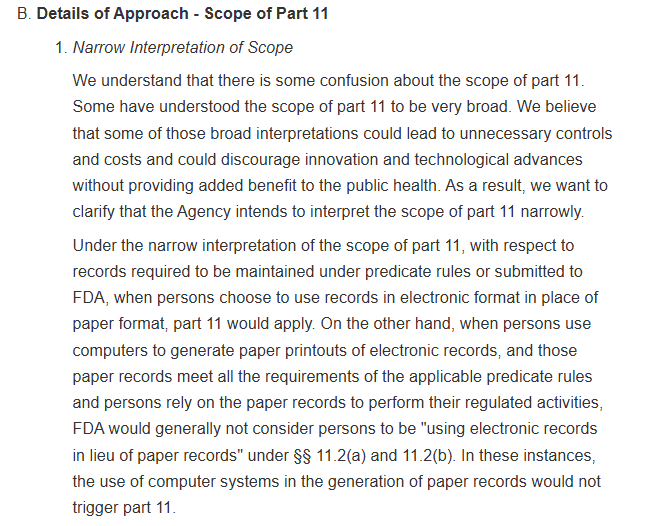
Do not require or advertise “Part 11 compliance” for every knowledge article. Identify which controlled records, approvals, signatures, training evidence, or regulated activities are in scope, then test the relevant controls and supporting procedures.
The knowledge base should not replace the system of record
An industry-specific knowledge base normally provides reusable guidance: approved procedures, explanations, troubleshooting, playbooks, policy interpretation, and decision support. It should not automatically become the repository for every transactional or case-specific record.
| Information type | Likely home | Role of the knowledge base |
|---|---|---|
| Reusable approved procedure | Knowledge base or controlled-document system | Explain the procedure and guide the user to the current approved version |
| Patient, student, customer, or client record | Authorized system of record | Explain how authorized users complete the workflow without copying case data into general content |
| Machine or asset state | MES, EAM, CMMS, PLM, or asset registry | Provide the procedure selected for the verified asset and operating context |
| Quality record or regulated approval | QMS or validated records system where required | Surface approved guidance and link to the controlled record |
| Support ticket or legal matter history | Ticketing, CRM, or matter-management system | Provide reusable answers while keeping case facts in the authorized workflow |
| Generated AI answer | AI interaction layer and logs | Ground the answer in current approved sources and preserve citations and permissions |
The safest design usually leaves authoritative transactional data in its source system and brings only the minimum verified context into the knowledge experience.
Build an industry content model before configuring search or AI
Industry fit depends on structured content. A platform should support the attributes needed to decide whether a document applies, who may see it, which version is current, and which source is authoritative.
Potential metadata includes:
- Audience, role, group, and competency level.
- Process, task, product, service, asset, machine, component, and site.
- Practice area, jurisdiction, contract, region, and language.
- Product, procedure, policy, or API version.
- Effective date, expiration date, review date, and end-of-support date.
- Owner, reviewer, approver, and source of authority.
- Approval state, evidence, sensitivity class, and retention class.
- Related system of record, superseded article, and escalation boundary.
Determine which fields are required, who owns their values, which values come from controlled vocabularies, and how changes propagate to search, portals, integrations, translations, and AI retrieval.
Do not rely on an AI model to infer critical authorization, jurisdiction, approval, retention, or product-version metadata. Those fields should come from governed content and trusted business systems.
Test search with industry language, not article titles
Industry users rarely search using the exact title selected by a documentation team. They use symptoms, abbreviations, part numbers, customer language, local site names, policy phrases, error codes, acronyms, and terms that may have several meanings.
Evaluate whether the platform supports:
- Controlled vocabularies and industry taxonomies.
- Synonyms, acronyms, aliases, and local terminology.
- Product, asset, location, version, and jurisdiction filters.
- Current-version and authoritative-source ranking.
- Permission-aware result titles and snippets.
- Multilingual terms and translated synonyms.
- Zero-result analysis and query reformulation.
- Relevance tuning without exposing restricted content.
Build the test set from real, de-identified searches, support questions, field terminology, and common misunderstandings. A demonstration using exact article titles proves very little about operational findability.
Strong search cannot make an obsolete or unapproved document trustworthy. Retrieval quality and content governance must be evaluated together.
Evaluate governance, lifecycle, and evidence
A specialized knowledge environment may need more than drafts and revision history. Buyers should determine what evidence the organization must retain about creation, review, approval, distribution, acknowledgment, change, supersession, archiving, and disposal.
| Capability | What it proves | What it does not prove by itself |
|---|---|---|
| Version history | Different saved versions existed | That the history is a complete, tamper-resistant audit trail |
| Approval workflow | A defined reviewer or approver completed a workflow action | That the approver was qualified or the process met a regulatory requirement |
| Effective date | When a version should become operational | That every user received or followed it |
| Acknowledgment | A user confirmed receipt or review | Training comprehension or competency |
| Electronic signature | A recorded signing action under defined controls | That the signature satisfies every applicable legal or regulatory requirement |
| Retention label | A configured lifecycle or preservation rule | That the configuration matches the applicable records schedule |
| Audit log | Recorded system events | Completeness, immutability, usability, or the required retention period |
Evaluate risk-based review paths, article ownership, effective dates, comparison and rollback, superseded relationships, deprecation, archive, legal hold, export, deletion, translation lifecycle, and change notifications.
Security and privacy must cover every delivery channel
Permissions should not stop at the article page. Test the complete path through search, snippets, recommendations, APIs, analytics, exports, direct URLs, chatbots, citations, caches, and connected AI systems.
Potential requirements include:
- SSO through SAML or OIDC.
- MFA and automated provisioning or deprovisioning.
- Role- and attribute-based access control.
- Article-, folder-, collection-, field-, or tenant-level permissions.
- Guest and external-user controls.
- Tenant isolation.
- Search-result security trimming.
- Permission-aware snippets and AI retrieval.
- Audit and administrative activity logs.
- Encryption and key-management options where required.
- Data classification, retention, deletion, residency, and subprocessors.
- Incident response, backup, recovery, API security, and offboarding.
NIST’s ABAC guidance describes authorization based on attributes associated with the subject, object, requested operation, and environmental conditions. Attribute-based rules can be useful when access depends on factors such as site, region, matter, contract, product, or competency, but the policy model and source attributes still need governance.
Compliance claims require scope and shared-responsibility analysis
A platform feature, certification, or security report can support a compliance program. It does not make the customer’s implementation compliant automatically.
Distinguish among:
- Documented product capability.
- Vendor certification or assessment scope.
- Contractual commitment.
- Applicable law, regulation, professional rule, or standard.
- Customer configuration and integrations.
- Customer procedures, monitoring, training, and records.
- Qualified legal, security, privacy, safety, compliance, or records validation.
A SOC 2 report is not a law. A FedRAMP-certified cloud service still operates within agency shared responsibility. A product marketed to healthcare does not guarantee that the customer’s use satisfies HIPAA. WCAG conformance cannot be established solely by an automated scanner. An FDA-related electronic-record claim is not meaningful until the applicable record and predicate-rule scope are identified.
For payment-related environments, the PCI Security Standards Council describes PCI DSS as a baseline of technical and operational requirements for entities that store, process, or transmit payment-account data or can affect the cardholder-data environment. Avoid copying cardholder data into general knowledge articles unless the architecture and use are explicitly approved.
Evaluate integrations by behavior, not by logos
The platform may need to connect with EHR, CRM, ITSM, DMS, ECM, QMS, PLM, MES, CMMS, EAM, ERP, LMS, HRIS, legal matter management, identity, records management, translation management, enterprise search, or an asset registry.
For every important integration, confirm:
- Whether it is native, API-based, embedded, federated, indexed, custom, or third-party.
- Which records and fields are read, written, or copied.
- Whether the flow is one-way or two-way.
- Which system remains authoritative.
- How permissions are mapped and synchronized.
- How quickly changes appear.
- What happens when the integration fails.
- Which actions are logged.
- Whether rate limits or plan restrictions apply.
- How data is exported and deleted.
- Whether the integration creates another uncontrolled copy.
A vendor logo confirms marketing recognition, not integration depth. The pilot should validate the exact workflow and failure behavior required by the organization.
Test frontline, mobile, offline, and shared-device use in the real environment
Manufacturing, utilities, aviation, construction, hospitality, retail, healthcare operations, and field-service teams may use knowledge under conditions very different from a desktop office.
- Test the actual phones, tablets, kiosks, rugged devices, or shared terminals.
- Test slow, intermittent, and unavailable network conditions.
- Confirm what remains accessible offline and how it synchronizes after reconnection.
- Evaluate QR, barcode, asset, machine, location, or work-order lookup.
- Check sign-in, timeout, and offboarding behavior on shared devices.
- Assess readability under time pressure, glare, gloves, noise, or limited-input conditions.
- Verify warnings, ordered steps, stop conditions, and escalation paths.
- Confirm how locally cached sensitive content is protected and removed.
A responsive website is not the same as a validated mobile or offline workflow. The device, network, identity, content, and operational context must be tested together.
Accessibility and localization are operational requirements
Industry knowledge may serve employees, customers, patients, students, citizens, partners, or contractors with different languages and access needs.
Evaluate translation workflows, source-to-translation change tracking, locale-specific approvals, multilingual search, language fallback, right-to-left support, and regional variations in terminology, policy, dates, units, and formats.
WCAG 2.2 defines testable accessibility requirements for web content and is intended to be evaluated through a combination of automated testing and human assessment. Test keyboard operation, screen-reader behavior, focus visibility, headings, landmarks, zoom, text resizing, contrast, captions, tables, forms, touch targets, and interactive components.
Do not assume that translating article text automatically produces an accessible or operationally correct localized experience.
Deployment and data location should follow the risk model
Potential deployment patterns include multi-tenant SaaS, single-tenant SaaS, private cloud, on-premises, and hybrid models. The most restrictive option is not automatically the best one.
Evaluate:
- Data and backup regions.
- Processing locations and subprocessors.
- Encryption and key-management options.
- Network isolation and private connectivity.
- Availability architecture and published service commitments.
- Recovery objectives and testing evidence.
- Maintenance windows and incident history.
- Status-page transparency.
- Export, contract termination, and end-of-service provisions.
- The customer’s ability to operate the selected model safely.
An on-premises installation may increase control over infrastructure while transferring patching, monitoring, backup, security, capacity, and continuity responsibilities to the customer. Compare the full operating model rather than the hosting label alone.
Evaluate AI and RAG as a governed retrieval system
An industry-specific AI assistant needs more than industry vocabulary. It must retrieve authorized, approved, current, and contextually applicable evidence—and recognize when the available evidence is insufficient.
Test whether the system can:
- Authenticate the user before retrieval.
- Preserve source permissions and tenant boundaries.
- Filter by product, asset, site, version, jurisdiction, role, and sensitivity.
- Prefer approved and current sources.
- Show usable citations and source passages.
- Refuse when no approved answer exists.
- Escalate to a qualified person.
- Avoid combining procedures with incompatible scope.
- Identify obsolete, conflicting, or superseded sources.
- Log retrieval and answer behavior for evaluation.
- Allow administrators to disable or constrain AI.
- Remove deleted or retired content from search and vector stores.
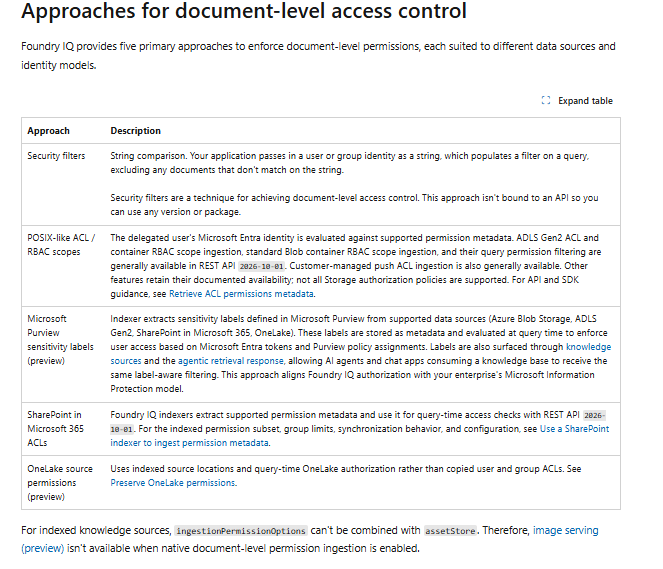
Azure AI Search documents several approaches to document-level access control, including security filters and preview capabilities that use source permission metadata. Availability and synchronization behavior vary by method and data source.
Amazon Bedrock documents ACL-aware retrieval but explicitly states that it is filtering rather than a complete authorization boundary. The application remains responsible for authenticating users and supplying verified identity context.
Build the evaluation set from realistic, de-identified questions:
- Common questions with one approved answer.
- Ambiguous industry terms.
- Procedures with similar names but different assets, products, or jurisdictions.
- Questions containing restricted information.
- Requests outside the user’s competency or authority.
- Outdated and superseded sources.
- Conflicting sources.
- Questions that require refusal or escalation.
RAG does not eliminate hallucinations. Citations do not prove correctness. A model connected to a knowledge base does not become compliant or professionally qualified.
Use mandatory gates before weighted scoring
Some requirements should eliminate a platform regardless of its editor quality, AI features, popularity, or price.
- The permission model can represent the required audiences, roles, sites, matters, customers, or tenants.
- Search titles, snippets, related content, APIs, exports, and AI answers enforce those permissions.
- Approval, effective date, version, rollback, and audit evidence meet the operating requirement.
- The required systems of record can be integrated without uncontrolled duplication.
- Data location, processing, deletion, security, and contract terms pass review.
- The required deployment model is available and supportable.
- Accessibility can be tested successfully.
- Required mobile, offline, QR, shared-device, or field workflows are viable.
- The platform supports the required language, region, and version model.
- Content, metadata, attachments, and useful history can be exported.
- The vendor can provide the required assurance, security, privacy, and procurement evidence.
- AI retrieval preserves authorization and can refuse unsupported questions.
A platform that fails a mandatory confidentiality, safety, records, or audit requirement should not win because it has a more attractive interface or lower subscription price.
Use weighted scoring only after the gates are passed
The following weights are illustrative, not an industry standard. Adjust them to the organization’s actual risk and workflow.
| Evaluation dimension | Illustrative weight | Evidence to collect |
|---|---|---|
| Security, permissions, and tenant isolation | 15% | Negative permission tests, identity documentation, audit evidence |
| Governance and auditability | 15% | Workflow demonstration, version history, effective dates, exportable logs |
| Search and domain vocabulary | 12% | Fixed query set using real sector terminology |
| Industry integrations | 12% | Working integration with documented data flow and failure behavior |
| Frontline, accessibility, and localization | 10% | Device testing, offline tests, accessibility review, locale workflow |
| AI reliability and retrieval controls | 10% | Evaluation set, citations, refusal tests, permission tests |
| Authoring and review workflow | 8% | Representative author, reviewer, approver, and rollback tasks |
| Deployment and reliability | 8% | Architecture, recovery, maintenance, and incident evidence |
| Portability and administration | 5% | Export test, configuration ownership, administration effort |
| Total cost | 5% | Subscription, implementation, integration, labor, and exit costs |
Define each score and preserve the evidence behind it. Do not allow a high average to hide failure of a mandatory gate.
Include these questions in the RFP
- Which industry workflows are supported through documented product capabilities?
- Which templates, schemas, taxonomies, and integrations are included?
- Which capabilities are generally available, preview, beta, custom, or partner-built?
- Can customers create controlled metadata and vocabularies?
- Can rules use role, group, asset, site, product, version, region, contract, customer, or jurisdiction?
- How are ownership, approval, effective dates, acknowledgments, retirement, and archiving handled?
- Which events are captured in the audit log, and can the log be exported?
- Which identity, SSO, MFA, and provisioning standards are supported?
- How are permissions applied to search, snippets, APIs, exports, analytics, and AI?
- What happens when a user changes role, group, matter, site, or employment status?
- Can external and internal audiences be supported safely in the same environment?
- Does the platform support mobile, offline, QR, kiosk, barcode, or shared-device use?
- Which systems of record have documented integrations?
- What data is copied, indexed, cached, or retained outside the source system?
- How quickly do content and permission changes synchronize?
- Which deployment models and data regions are available?
- Which security, privacy, assurance, and incident documents can the vendor provide?
- How are backup, recovery, deletion, retention, and contract termination handled?
- Can the complete knowledge base be exported with metadata, attachments, translations, redirects, and useful history?
- How are translations, regional variants, and product versions governed?
- How is AI enabled, disabled, evaluated, logged, and monitored?
- Which data is sent to AI subprocessors, where is it processed, and how long is it retained?
- Is customer content used to train general-purpose models?
- How are deleted or retired documents removed from search and vector stores?
- Which implementation, migration, customization, training, and support services are included?
- What administration work remains with the customer?
- How are users, storage, AI usage, API usage, and support priced?
Run a realistic proof of concept
A vendor-controlled demonstration is useful for orientation but insufficient for selection. The pilot should use one defined industry workflow, representative users, approved de-identified or synthetic content, real metadata, required integrations, and a fixed evaluation set.
- Author and approve content. Create a representative article with owner, source, version, effective date, audience, and risk metadata.
- Test lifecycle control. Compare versions, roll back a change, supersede an article, and verify the audit evidence.
- Test search. Use industry terms, acronyms, synonyms, misspellings, codes, and user language.
- Test permissions positively. Confirm that authorized users receive the correct article, snippet, attachment, and AI answer.
- Test permissions negatively. Confirm that similar but unauthorized users receive no title, snippet, citation, direct-link access, API result, or export.
- Test the integration. Change a relevant record or permission in the source system and observe the documented synchronization behavior.
- Test frontline delivery. Use the actual mobile, shared, kiosk, QR, or offline workflow where applicable.
- Test accessibility. Include keyboard, screen-reader, zoom, focus, contrast, form, and touch-target checks.
- Test AI answers. Include correct, ambiguous, outdated, restricted, conflicting, unsupported, and escalation-required questions.
- Test translation and regional variants. Update the source and verify the locale workflow, search, and fallback.
- Test retirement. Archive or delete an article and verify its removal from search, recommendations, AI, integrations, and exports as intended.
- Test portability. Export representative content, metadata, attachments, translations, and history.
- Measure administration effort. Record the work required to maintain roles, taxonomies, workflows, integrations, and evaluations.
Define success and failure thresholds before the pilot begins. A proof of concept has not succeeded merely because the platform can display the content.
Calculate total cost beyond the subscription
The lowest license price may create the highest operating cost if the organization must build missing controls, maintain custom integrations, or manually verify critical workflows.
Include:
- Subscriptions and additional user types.
- External, read-only, or frontline users.
- AI, storage, API, and search usage.
- Implementation and migration.
- Content cleanup and classification.
- Taxonomy and metadata design.
- Workflow and permission configuration.
- Custom development and integrations.
- Identity, security, privacy, and compliance review.
- Accessibility remediation and localization.
- Mobile, offline, kiosk, or shared-device deployment.
- Training and change management.
- Ongoing administration and audit support.
- Sandbox or test environments.
- Backup and disaster-recovery requirements.
- Export, exit, and future migration.
- Customization maintenance after upgrades.
Separate the subscription cost from implementation cost, internal labor, ongoing administration, customization debt, unused capacity, and the cost of leaving the vendor later.
When industry-specific software is a strong fit
- Incorrect knowledge can create safety, privacy, financial, legal, or operational harm.
- Different roles, jurisdictions, assets, sites, or products require different guidance.
- Controlled procedures and review evidence are required.
- Users need mobile, offline, QR, kiosk, or shared-device delivery.
- Industry systems of record must supply verified context.
- Several active product or procedure versions must be maintained.
- Search must understand specialized vocabulary.
- AI requires current, approved, permission-aware sources.
- The organization can provide ownership and governance for the configuration.
When a standard platform may be enough
- The content is low risk and not case-specific.
- One team manages a small, stable collection.
- Most users require the same answer.
- Industry terminology is limited.
- Complex approval, retention, or audit controls are unnecessary.
- Few integrations are required.
- A standard wiki already supports the workflow.
- Users can easily escalate unusual or high-risk questions.
- The cost of customization would exceed the expected value.
Do not buy specialized software to avoid fixing weak ownership, stale content, or poor governance. A more sophisticated platform will distribute poor knowledge more efficiently unless those foundational problems are addressed.
Common selection mistakes
Choosing a vendor because it has an industry landing page
Translate the industry problem into testable controls, integrations, metadata, and delivery requirements before comparing vendors.
Treating badges as proof of a compliant implementation
Review the assessed service, report scope, customer responsibilities, configuration, contract, and intended data flow.
Treating the knowledge base as the system of record
Keep transactional and case-specific records in their authorized source systems, and use the knowledge base for reusable approved guidance.
Ignoring search vocabulary
Build the test set from real industry language, abbreviations, codes, symptoms, and local terminology rather than exact article titles.
Testing only administrator accounts
Use ordinary users, external users, restricted groups, recently changed roles, offboarded identities, and cross-tenant scenarios.
Evaluating integrations by logo
Test the actual data flow, permissions, synchronization, error handling, audit trail, deletion, and recovery behavior.
Assuming responsive design solves frontline access
Test the real device, network, sign-in, offline, shared-device, and local-cache conditions.
Buying AI before governing the content
Define owners, sources, approval, versions, permissions, retirement, and evaluation before using the content for generated answers.
Comparing license prices instead of total cost
Include implementation, integrations, internal labor, administration, accessibility, localization, audit support, and exit.
Frequently asked questions
What is industry-specific knowledge base software?
It is a knowledge platform designed or configured around a sector’s terminology, entities, roles, workflows, systems of record, risks, approval requirements, records obligations, delivery conditions, and retrieval constraints.
Does industry-specific software guarantee compliance?
No. Software may provide controls, certifications, reports, or contractual commitments that support a compliance program. Compliance also depends on the applicable requirements, configuration, integrations, data, procedures, monitoring, training, and customer responsibilities.
Is a vertical platform better than a configurable platform?
Not automatically. A vertical platform may reduce domain configuration, while a configurable platform may better support several departments or industries. Compare mandatory controls, integration effort, maintainability, portability, and total cost.
Can one platform support several industries or business units?
It can when the platform supports separate taxonomies, roles, workflows, permissions, content models, integrations, and governance boundaries. Shared infrastructure should not erase meaningful operational or confidentiality differences.
When is a standard wiki enough?
A standard wiki may be sufficient for low-risk, stable knowledge used by a relatively homogeneous team with limited integrations and simple review requirements. It becomes less suitable as the cost of incorrect, unauthorized, obsolete, or inaccessible guidance increases.
Does the knowledge base replace an EHR, QMS, PLM, DMS, or CRM?
Usually not. The knowledge base provides reusable approved guidance, while those systems manage authoritative records, transactions, controlled documents, assets, cases, or customers. Integration should preserve the responsibility of each system.
How should AI be evaluated?
Test permission-aware retrieval, current and approved sources, metadata filtering, citations, conflicting content, refusal, escalation, tenant separation, deleted-content handling, and realistic industry questions. Do not rely on a polished vendor demonstration.
Does a regulated organization always need on-premises software?
No. The appropriate deployment depends on the security model, applicable requirements, data location, integrations, staffing, vendor evidence, operating capacity, and risk decision. On-premises deployment also transfers substantial operational responsibility to the customer.
What should be tested first?
Test mandatory requirements first: permissions, search and snippet security, governance evidence, required integrations, deployment, accessibility, frontline use, export, and AI authorization. Evaluate convenience features only after those gates pass.
Choose the operating model before choosing the software
Industry-specific knowledge base software should be selected from the organization’s risks, users, terminology, workflows, systems, evidence requirements, and delivery environment—not from the industries listed on a vendor’s homepage.
Define mandatory gates, map the systems of record, create the domain metadata, test search using real language, validate permissions across every delivery channel, and run a pilot with representative devices and workflows. Only then should the organization compare convenience, design, and price.
The best solution may be a vertical product, a configured general platform, a module inside an existing suite, or a composable architecture. The correct choice is the one that can deliver current, authorized, explainable knowledge while remaining governable, supportable, accessible, and affordable over time.